
Share with your CISO
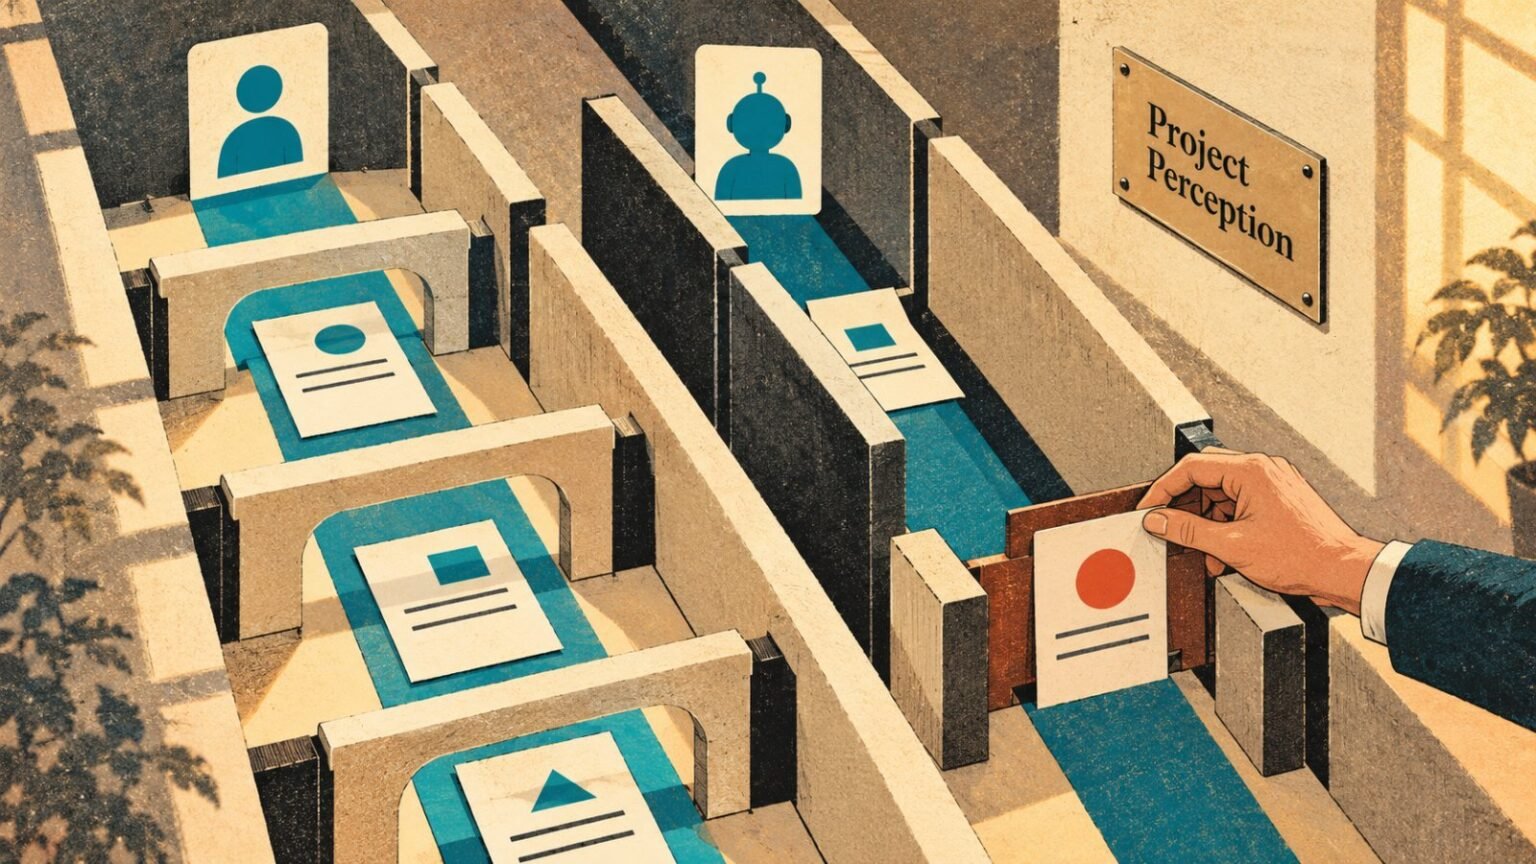
Microsoft is treating AI agents the way it treats human insiders, building a supervision layer called Guardian Agents that sits outside the models it watches, because the company’s own security leadership concedes frontier models “cannot be trusted.” The October 2026 expansion of Project Perception adds a shared registry, per-agent identities through Microsoft Entra Agent ID, and dynamic permissions that expire with the task. Discovery grows from 35 to 60 local agent types. The full Guardian Agents architecture remains invitation-only preview with no general availability date.
What this means for your business
The dividing line here is whether your organization has already deployed agents you didn’t centrally provision. Enterprises that let business units or individual employees spin up agents through Copilot Studio or third-party tools almost certainly have undiscovered agents acting on employee credentials right now, inheriting permissions those employees never intended to delegate. If your identity governance program doesn’t enumerate agents separately from human users, you have an attribution gap, and Microsoft’s announcement is effectively a public acknowledgment that this gap is the industry’s most pressing unsolved problem.
The architecture Microsoft describes solves a specific failure mode that has no widely adopted name yet: permission laundering, where an agent inherits the full access scope of its human sponsor and then exercises it autonomously, without the judgment, accountability, or audit trail the original permission grant assumed. Dynamic Permissions and the Execution Container boundary are designed to interrupt that chain. The enforcement logic sits outside the model being governed, which is the right call, because a model that can also evaluate its own access requests is not a control at all. The design is sound. The gap is that “announced design” and “enforceable safeguard” are not the same thing until the integrations ship with stated availability dates.
The vendor frame matters here. Microsoft has every incentive to accelerate enterprise agent adoption, and framing Guardian Agents as the answer to agent risk is a way to make the Microsoft stack the least-scary place to deploy agents. That incentive tilts the announcement toward architectural completeness on paper and optimistic timelines in practice. CISOs who treat this as a solved problem because it’s been announced will be wrong. The falsification condition is simple: if a discovered agent can receive an Entra identity that flows through to an enforceable Dynamic Permissions change inside your existing tenancy, the control chain works. Until that end-to-end path has a general availability date, your governance posture should reflect the preview status, not the press release.
Concept deep-dive: Least-privilege enforcement for AI agents
Least-privilege is the security principle that any actor, human or automated, should hold only the permissions needed for the specific task at hand, nothing broader. For human users, it’s enforced at provisioning time. For agents, the challenge is that tasks change mid-run, so a static permission grant is either too broad from the start or constantly requires human re-approval. Dynamic Permissions attempts to make least-privilege time-bound and task-scoped, shrinking or revoking access as the work evolves, which is the missing mechanism between agent deployment and genuine access governance.
Based on reporting from Microsoft Guardian Agents to Supervise Enterprise AI Agents, originally published 2026-10-21 20:05:00.