
Share with your CISO
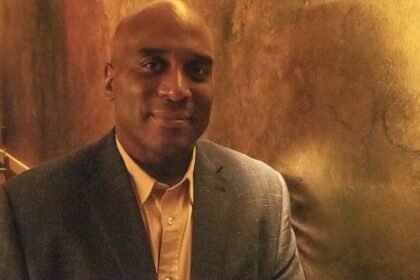
Confide, founded by Wirecard whistleblower Pav Gill, is betting that enterprise GRC (governance, risk, and compliance, the systems that track policy, audit, and accountability across an organization) is fundamentally broken and that agentic AI makes the problem urgent enough to force a rethink. The new platform unifies case management, policy, risk, and audit in a single record, and extends that governance model to cover AI agents alongside human employees, with every action logged in a defensible audit trail.
What this means for your business
The question worth asking isn’t whether your GRC stack is fragmented, it almost certainly is. The question is whether that fragmentation was tolerable when the actors were all human and becomes genuinely dangerous when AI agents start initiating workflows, processing incident reports, and making low-level decisions your team never reviews. CISOs whose audit trails currently live across five tools should treat Confide’s pitch less as a vendor announcement and more as a diagnostic: if a serious incident happened tomorrow, could you reconstruct the full decision chain without a manual investigation spanning multiple systems?
Pav Gill’s Wirecard credibility is real, but it cuts two ways. His lived experience of catastrophic governance failure gives the product a sharper design brief than most GRC vendors ever have, and the Wirecard collapse is a genuinely instructive case, where fragmented data and lax oversight allowed a decade of fabricated revenue to go undetected. The risk is that the founding story also becomes the entire marketing thesis, papering over the harder questions: how does Confide handle integrations with existing identity and access management systems, what does the AI agent governance model look like under regulatory scrutiny, and who are the design partners that stress-tested the product before launch?
The deeper issue Confide is pointing at is real and underpriced by most security teams right now. As agentic AI systems move from pilots into production, the governance gap between “what humans are permitted to do” and “what AI agents are permitted to do” is widening fast, and existing GRC tools weren’t designed to close it. The vendor that wins this space won’t be decided by founding story or positioning, it’ll be decided by which platform earns its place inside the first major regulatory investigation where an AI agent was a named actor in the incident. That case hasn’t happened publicly yet, but it will, and the audit trail question it raises is already a budget decision your team can make before the incident does it for you.
Based on reporting from Wirecard whistleblower Pav Gill launches new AI governance, risk and compliance platform, originally published 2026-10-06 03:23:00.